custom CVE-2026-34621 ClamAV signature
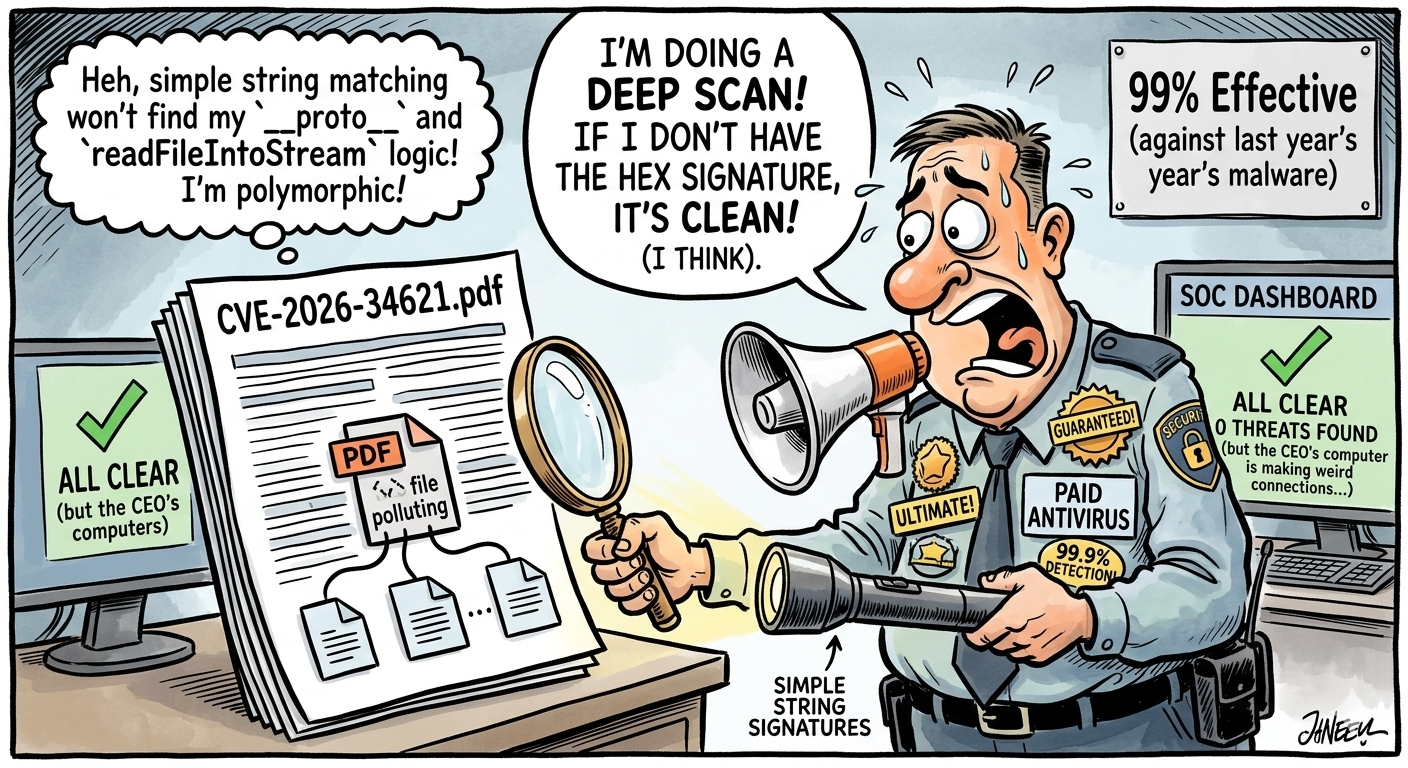
CVE-2026-34621
Adobe has released a security update for Adobe Acrobat and Reader for Windows and macOS. This update addresses a critical vulnerability. Successful exploitation could lead to arbitrary code execution.
Adobe is aware of CVE-2026-34621 being exploited in the wild.
Test I have done
Using python, I have inserted a Java Script payload into a pdf file and confirmed the vulnerability.
I also tested several paid antivirus solutions but no detections.
plan of action
Get the job done
As a sysadmin inside a large company, I wanted to protect the email server spreading this kinda PDF’s towards inboxes.
Inside ClamAV i have wrote a custom ldb file with a trivial signature, looking for some specific tags :
					Exploit.PDF.CVE_2026_API:0:*:7574696c*7265616446696c65496e746f53747265616d
Exploit.PDF.CVE_2026_Proto:0:*:5f5f70726f746f5f5f
Exploit.PDF.CVE_2026_OctalProto:0:*:5c3133375c31333770726f746f5c3133375c313337
1. Different Encoding/Compression
As you saw, pypdf used octal encoding (\056). However, a real-world exploit for CVE-2026-34621 would likely use FlateDecode (zlib compression).
When a stream is compressed, the strings
util.readFileIntoStreamand__proto__completely disappear from the file’s binary data.ClamAV cannot “see” inside the compressed stream unless it has a specific engine to decompress PDF objects on the fly (which it does, but it can be bypassed with “filter chaining” like
/FlateDecode /ASCII85Decode).
2. Hex Encoding in Tags
I searched for /JavaScript in hex (2f4a61...). An attacker can change that tag to:
/J#61vaScript/JS/Java#53criptAll of these are valid in Adobe Acrobat, but each one would break your current signature.
3. JavaScript Obfuscation
Inside the script itself, an attacker won’t write __proto__. They will use JavaScript’s ability to build strings dynamically:
JavaScript
var p = "__pro";
var t = "to__";
var exploit = object[p + t]; // ClamAV will never see the full string
we are part of the family. all the way through.
## insert this into  /var/lib/clamav/cve_2026_34621.ldb
CVE_2026_PDF_Exploit;Target:0;0&1&(2|3);2f4a53;2f4a617661536372697074;7265616446696c65496e746f53747265616d;7574696c5c3035367265616446696c65
## Save it
chown clamav:clamav /var/lib/clamav/cve_2026_34621.ldb
## Test it
clamscan -d /var/lib/cve_2026_34621.ldb /root/cve_test_sample.pdf
/root/cve_test_sample.pdf: CVE_2026_PDF_Exploit.UNOFFICIAL FOUND

----------- SCAN SUMMARY -----------
Known viruses: 1
Engine version: 0.103.12
Scanned directories: 0
Scanned files: 1
Infected files: 1
Data scanned: 0.00 MB
Data read: 0.00 MB (ratio 0.00:1)
Time: 0.005 sec (0 m 0 s)
Start Date: 2026:04:14 17:20:31
End Date:   2026:04:14 17:20:31